


Data protection in cloud environments is no longer optional-it is a mandatory requirements across public, multi and hybrid cloud setups. However, baseline protection falls short of satisfying the strict regulatory demands governing modern industries.
As cyberthreats multiply, securing digital information has become more critical than ever. The lurking danger even accelerates with the adoption of AI and the advent of Quantum Computing.
As cyber threats multiply, securing digital information has reached a critical tipping point. The danger accelerates rapidly as organizations adopt Artificial Intelligence (AI) and prepare for the looming reality of Quantum Computing.
Here is a closer look at how General Purpose Hardware Security Modules (GP HSM) and Key Management Systems (KMS) provide the reliable foundation for data security and sovereignty in the cloud.
Securing the Cloud with Strong Cryptographic Control
The future of cloud data protection and sovereignty relies on four pillars: control, resilience, adaptability, and compliance. GP HSMs serve as the root of trust, while KMS act as the central access and control panel.
Combining these solutions creates a powerful defense against current cloud security challenges while providing the strength needed to neutralize tomorrow’s threats.
HSMs: The Root of Trust for Data Governance
Effective data security governance requires securing information through strong encryption, protecting it at every access point, and proving regulatory compliance.
Achieving this level of governance requires the right tools. HSM-based encryption offers the most reliable way to apply cryptographic security, providing superior capabilities for creating and storing high-quality encryption keys. Functioning as a hardware-based vault, an HSM stores keys inside secure physical boundaries, making it the ideal root of trust for all encryption operations.
KMS: Centralized Encryption Key Management
Encryption is only as strong as the security of the keys that guard it. Given the complex nature of modern cloud deployments, centralizing key management through a single pane of glass is no longer a luxury—it is the backbone of a resilient cybersecurity strategy.
Poor key management easily leads to data breaches and existential business threats. A highly secure KMS significantly reduces these risks by enforcing strict access controls. It prevents unauthorized access while ensuring authorized entities can manage and retrieve keys efficiently.
Additionally, a robust KMS provides full traceability. Knowing exactly who accessed specific data and when creates a complete audit trail, simplifying compliance with security policies and regulatory frameworks.
Uniting Cloud Flexibility with Cryptographic Power
Organizations face an ongoing challenge: navigating local compliance regulations while maintaining tight security across complex, multi-jurisdictional cloud environments. Data collected, processed, or stored in different regions remains subject to a wide variety of localized laws.
At Utimaco, data protection and cloud sovereignty are not just checkboxes. We deliver powerful cybersecurity solutions that enable secure cloud deployments. Our tools empower organizations to stay compliant while acting as a reliable shield against complex threat landscapes.
Utimaco HSMs and KMS: The Bedrock of Cloud Security and Data Sovereignty
Utimaco’s General Purpose HSMs generate and protect keys according to the highest security standards, laying the groundwork for robust data security governance. Organizations across all industries utilize this cryptographic power to secure sensitive data and easily manage security policies across any cloud environment.
We offer top-tier protection alongside flexible deployment options. You can host a physical appliance in your own environment or choose a cloud-hosted, hardware-based as-a-Service offering located in our certified data centers.
See how our GP HSMs can build the foundation for your data governance strategy.
→ Learn more about our HSM portfolio here
Utimaco’s Key Management Systems deliver a holistic, highly secure key management strategy. The centralized management approach handles all encryption keys throughout their complete lifecycle, ensuring your organization retains full control at all times. Our centralized KMS platforms act as your data governance engine—granting access only to authorized users, blocking unauthorized entry, and enforcing security standards in real-time.
Aligning with our customer-centric approach, we offer these solutions as physical or virtual appliances for on-premises operation, or as a flexible, cloud-enabled as-a-Service deployment based on our high-security physical infrastructure.
Discover our KMSs providing the central key access and control panel.
→ Learn more about our KMS portfolio here
Defending Against AI and Quantum Computing Threats utilizing the capabilities of Utimaco’s HSMs and KMS
While quantum computing might feel futuristic, AI is already deeply embedded in business operations. AI models can cause severe data loss or exposure due to governance gaps, silent failures, or direct compromises. Fortunately, you can easily elevate your AI security posture using GP HSM and KMS solutions.
In this context, our HSMs provide a hardware-backed root of trust, establishing a non-negotiable foundation for identity, integrity, and confidentiality across the AI lifecycle. Meanwhile, our KMS platforms serve as the single-access control plane, defining exactly who or what can access data, models, and execution environments. The system itself enforces trust through strict cryptographic verification before permitting any sensitive operations.
→ Read our Blog Post “AI Security Isn’t About Models, it is About Governance” here to discover how our solutions enable your AI security strategy.
Regarding Quantum Computing, the clock is ticking. Industry leaders are already preparing; Cloudflare, for instance, recently moved its post-quantum cryptography (PQC) deadline forward to 2029 (read more about it here).
Regardless of the exact timeline, the impact on encryption is already a reality due to the "Harvest Now, Decrypt Later" (HNDL) threat. Future quantum advancements will likely render today’s encryption useless, exposing vast amounts of sensitive data. This affects both current data and information compromised years ago.
By adding Quantum Protect to your Utimaco GP HSM firmware, you can neutralize this threat. This capability allows your organization to swap encryption methods as standards evolve, seamlessly adopting post-quantum cryptography before current defenses fail.
Are you ready to take the next step?
Do not wait for compliance failures or next-generation threats to expose your vulnerabilities. Contact us today to explore how our HSMs and KMS can become the cornerstone of your cloud data security and data sovereignty strategy.
Prêt à assurer votre avenir numérique ?
Rejoignez plus de 500 entreprises mondiales et institutions gouvernementales qui font confiance à Utimaco pour leur infrastructure de sécurité critique.
Contacter le service des ventesYour download request(s):

Your download request(s):
About Utimaco's Downloads
Visit our Downloads section and select from resources such as brochures, data sheets, white papers and much more. You can view and save almost all of them directly (by clicking the download button).
For some documents, your e-mail address needs to be verified. The button contains an e-mail icon.
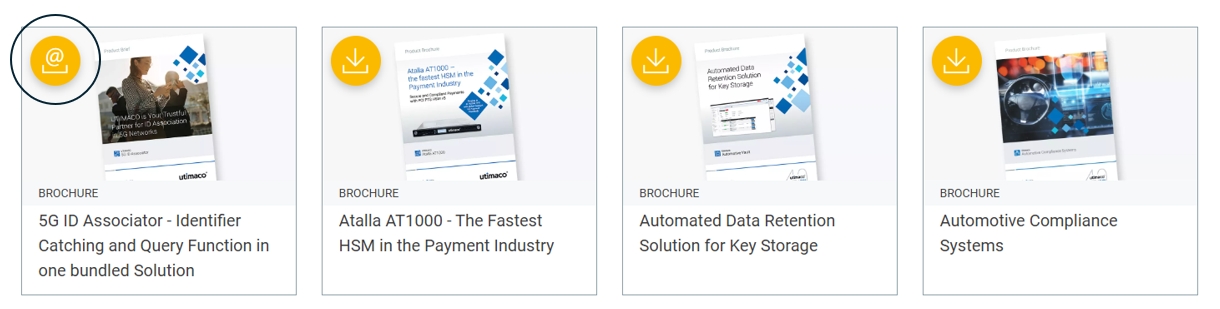
A click on such a button opens an online form which we kindly ask you to fill and submit. You can collect several downloads of this type and receive the links via e-mail by simply submitting one form for all of them. Your current collection is empty.