


Artificial Intelligence (AI) is reshaping how organizations create value, make decisions, and manage sensitive information. Yet in the rush to innovate, many overlook the fundamental truth: AI security is not about the sophistication of your model—it’s about your ability to govern access, authorization, and trust throughout the entire AI lifecycle. Real-world attacks don’t always target model accuracy or obvious flaws; they exploit gaps in authority, control, and oversight.
Governance as the Foundation of AI Security
As the volume and complexity of AI systems multiply, so do the risks. Without provable answers to questions like “Who can access which model or dataset—and under what conditions?”, confidence in AI becomes little more than wishful thinking.
Governance—not models or infrastructure—defines whether your AI is an engine for innovation or a source of unchecked risk.
Why AI Needs More Than Traditional Security
Conventional security approaches focus on perimeter defense, identity management, and infrastructure controls. But AI ecosystems are different: models are probabilistic, pipelines are dynamic, and data flows autonomously between services and clouds. Control cannot end at the network or application layer. Instead, it must be rooted in cryptographic governance—which is exactly what a Key Management System (KMS) delivers.
The Role of Key Management Systems in AI Governance
A modern KMS is far more than a tool for storing your keys. It is the operating system of trust, policy enforcement, and cryptographic authority across all dimensions of your AI landscape—from data to models, pipelines to inference. Here’s how a KMS brings governance, accountability, and provable control to AI use cases:
- Centralized Key Lifecycle Management:
The KMS manages the generation, rotation, revocation, and destruction of cryptographic keys in a central way, automatically aligning with business and regulatory requirements. Each action is logged in an immutable audit trail, empowering organizations to prove compliance and investigate incidents with confidence. - Policy-Based Key Authorization:
The KMS enforces granular access and usage policies for encryption keys. Every cryptographic operation—be it encrypting data, decrypting sensitive inputs for inference, or signing AI outputs—requires explicit, policy-approved authorization. This means only allowed users, models, or services can access or use keys for protected operations. - Orchestration of Encryption and Decryption Flows:
Sensitive data is shielded not just at rest or in motion, but also as it moves through AI training, inference, and post-processing. The KMS assures the right keys are used at the right moments, in the right places, and never outside authorized environments. - Governance Across Models and Pipelines:
Modern AI ecosystems involve many actors—models, microservices, data feeds, and cloud providers. The KMS acts as the single “control plane,” orchestrating who or what can retrieve cryptographic keys for which process or asset. This enforces isolation, separation of duties, and privilege access. - Seamless Integration for AI Services:
An ideal KMS supports standard APIs, such as KMIP, ensuring that AI workloads and machine actors can get approved key usage without bottlenecks or manual intervention. This keeps development agile but secure and keeps models and data governed even as environments scale and shift.
Achieving Provable Trust and Compliance in AI
Provable trust is not about trusting your model. It is about being able to verify— both cryptographically and audibly. It is about transparency which model, on which data, in which environment, and under what policies any given inference or decision was made. This is at the heart of responsible AI adoption and is increasingly demanded by regulations such as the EU AI Act and GDPR.
A capable KMS, operating as the orchestrator of trust, is critical for organizations seeking to:
- Demonstrate auditability for regulators and customers, with tamper-proof logs of every key access and cryptographic event.
- Respond rapidly to threats by revoking or rotating keys instantly across global environments.
- Enforce separation of duties between teams, engines, and services—mitigating risks of insider threat or shadow AI deployment.
- Adopt crypto agility and prepare for quantum-safe transitions, as new standards and algorithms become available.
Preparing Your AI for a Quantum-Resilient Future
The dual wave of AI adoption and looming quantum computing breakthroughs means that cryptographic infrastructure must be secure, resilient and adaptable. A KMS forms the trust-driven backbone for complete control over all cryptographic keys, enables seamless migration, allows to automate key rotation as standards evolve, and future-proofs sensitive workloads by utilizing keys based on post-quantum algorithms —without overhauling the stack.
Enable Your AI Security Strategy With Utimaco’s KMS Solutions
Utimaco’s KMS solutions drawing directly from current best practice and innovations in the AI field, reflected in their sophisticated technical features based on physical and logical capabilities.
Utimaco’s Enterprise Secure Key Manager (ESKM) and Enterprise Key Manager as a Service (EKMaaS) are designed to anchor trust and cryptographic governance deep within your AI stack. With centralized policy enforcement, role-based access, end-to-end key lifecycle management, and out-of-the-box integration for modern AI pipelines, our KMS offerings empower you to innovate responsibly while retaining full control and auditability. Whether you prefer to operate them on-premises or take advantage of an as a Service-offering. Our solutions enable you to meet regulatory demands, enforce crypto agility, and embed AI governance into your organizational DNA.
Unlock the potential of AI with confidence: assurance comes not just from brilliant models, but from bullet proof governance orchestrated by your KMS. Let’s put trust at the core of your AI journey—today and in the future.
Ready to Secure Your Digital Future?
Join over 500 global enterprises and government institutions who trust Utimaco for their critical security infrastructure.
Contact SalesYour download request(s):

Your download request(s):
About Utimaco's Downloads
Visit our Downloads section and select from resources such as brochures, data sheets, white papers and much more. You can view and save almost all of them directly (by clicking the download button).
For some documents, your e-mail address needs to be verified. The button contains an e-mail icon.
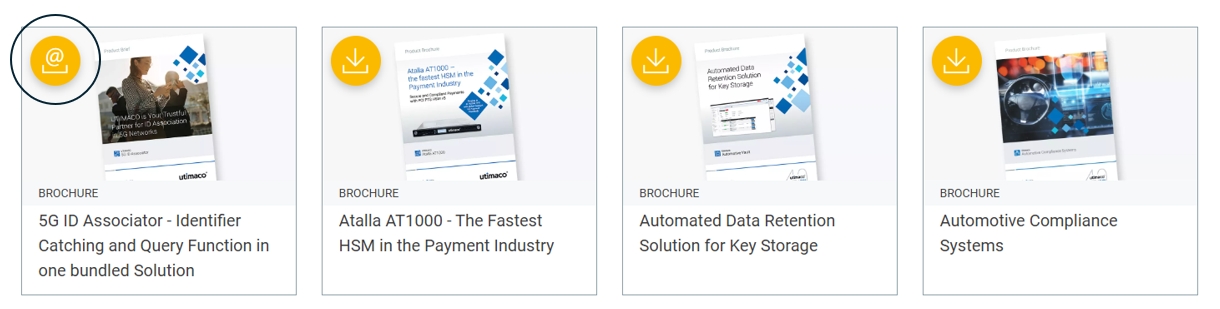
A click on such a button opens an online form which we kindly ask you to fill and submit. You can collect several downloads of this type and receive the links via e-mail by simply submitting one form for all of them. Your current collection is empty.